46°F

Aaron Parecki

  • Articles
  • Notes
  • Photos
  • AGNTCon + MCPCon North America

    Oct
    22
    Oct
    23
    October 22, 2026 at 8:00am (-0700)
    through October 23, 2026 at 5:00pm (-0700)
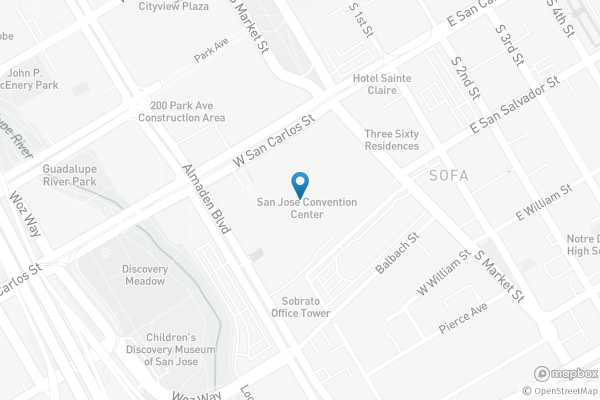
    San Jose McEnery Convention Center
    150 W San Carlos St, San Jose, California, US
    permalink #okta #mcp #mcpcon
    • Evolution, not Revolution: How MCP is Reshaping OAuth

      Oct
      22
      October 22, 2026
      10:35am - 11:00am (-0700)
      LL20A (Lower Level)
      AGNTCon + MCPCon North America
      The impulse to rewrite the auth stack for AI agents is strong, but we cannot design away the fundamental relationships standards protect. This session explores how MCP is reshaping OAuth—not abandoning it—to meet the ecosystem's unique challenges:

      The "Unregistered Client" Problem: Traditional OAuth requires pre-registration. MCP breaks this. We’ll see how Client ID Metadata Documents (CIMD) allow agents to bring their own identities to arbitrary servers, how it improves on Dynamic Client Registration, and how to mitigate the risks of unregistered clients.

      Separation of Concerns: Why your MCP server shouldn't be your Authorization Server. We’ll cover how Protected Resource Metadata (RFC 9728) enables dynamic auth server discovery, keeping agents lightweight and security boundaries clean.

      Enterprise-Managed Authorization: To stop "click-through fatigue," we’ll introduce the Identity Assertion Authorization Grant. This moves consent to the enterprise policy layer, enabling secure, scalable adoption.

      Join me to secure the agent ecosystem—from discovery to governance—not by reinventing the wheel, but by making incremental improvements to the way it turns.
      permalink #mcp #xaa #okta #oauth
    • How Open Standards Solve the Missing Identity Layer for AI Agents

      Oct
      23
      October 23, 2026
      10:55am - 11:20am (-0700)
      210A
      AGNTCon + MCPCon North America
      As AI agents transition from concept to autonomous enterprise tools, traditional access models are breaking down. Relying on legacy OAuth flows, static API keys, and service accounts that bypass Zero Trust controls creates shadow AI footprints, consent fatigue, and unmanageable identity sprawl. The industry needs open, vendor-neutral standards so applications and agents can securely establish trust across enterprise environments.

      In this session, identity standards experts Aaron Parecki and Danny Zollner will explore the emerging protocols that make secure, seamless AI interoperability possible. They will break down the rapid adoption of the Cross App Access (XAA) protocol, dive into the IETF’s Workload Authorization Grant (WAG) for agents operating on their own behalf, and examine why SCIM must evolve to enable provisioning and lifecycle management of agent identities. Join us to learn why cross-industry collaboration is essential, and how practitioners and vendors alike can help move the industry forward, rather than waiting for someone else to decide how agent identity works.
      permalink #okta #mcp #oauth
    • ID-JAG: Solving OAuth Sprawl for Enterprise AI Agents

      Oct
      23
      October 23, 2026
      1:45pm - 2:10pm (-0700)
      230C
      AGNTCon + MCPCon North America
      Enterprise AI agents are moving from demos into production, and auth is becoming a blocker. Demo agents can connect to tools with OAuth, but real enterprise agents may need SaaS services for thousands of employees. Per-user, per-service consent does not scale.

      This session explains ID-JAG, the Identity Assertion JWT Authorization Grant pattern behind MCP's Enterprise-Managed Authorization extension. ID-JAG turns an existing SSO login into centrally governed, auditable access to approved MCP servers, without repeated OAuth prompts.

      We'll cover the production problem, protocol flow, and lessons from implementing ID-JAG support in Archestra, one of the first MCP clients to support it. We'll also discuss what identity provider support enables.

      Attendees will leave with a model for production agent auth: one SSO login, centralized policy, scoped MCP-native access tokens, fewer consent screens, and a cleaner security review story.

      We'll close with the missing piece: SaaS provider adoption. To unlock enterprise deployments, authorization servers need to support this flow so agents can access approved business systems without key-sharing, manual credentials, or one-off integrations.
      permalink #okta #xaa #mcp #oauth
Posted in /events using quill.p3k.io

Hi, I'm Aaron Parecki, Sr Director of Identity Standards at Okta, and co-founder of IndieWebCamp. I maintain oauth.net, write and consult about OAuth, and participate in the OAuth Working Group at the IETF. I also help people learn about video production and livestreaming. (detailed bio)

I've been tracking my location since 2008 and I wrote 100 songs in 100 days. I've spoken at conferences around the world about owning your data, OAuth, quantified self, and explained why R is a vowel. Read more.

  • Sr Director of Identity Standards at Okta
  • IndieWebCamp Founder
  • OAuth WG Editor
  • OpenID Board Member

  • 🎥 YouTube Tutorials and Reviews
  • 🏠 We're building a triplex!
  • ⭐️ Life Stack
  • ⚙️ Home Automation
  • All
  • Articles
  • Bookmarks
  • Notes
  • Photos
  • Replies
  • Reviews
  • Trips
  • Videos
  • Contact
© 1999-2026 by Aaron Parecki. Powered by p3k. This site supports Webmention.
Except where otherwise noted, text content on this site is licensed under a Creative Commons Attribution 3.0 License.
IndieWebCamp Microformats Webmention W3C HTML5 Creative Commons
WeChat ID
aaronpk_tv