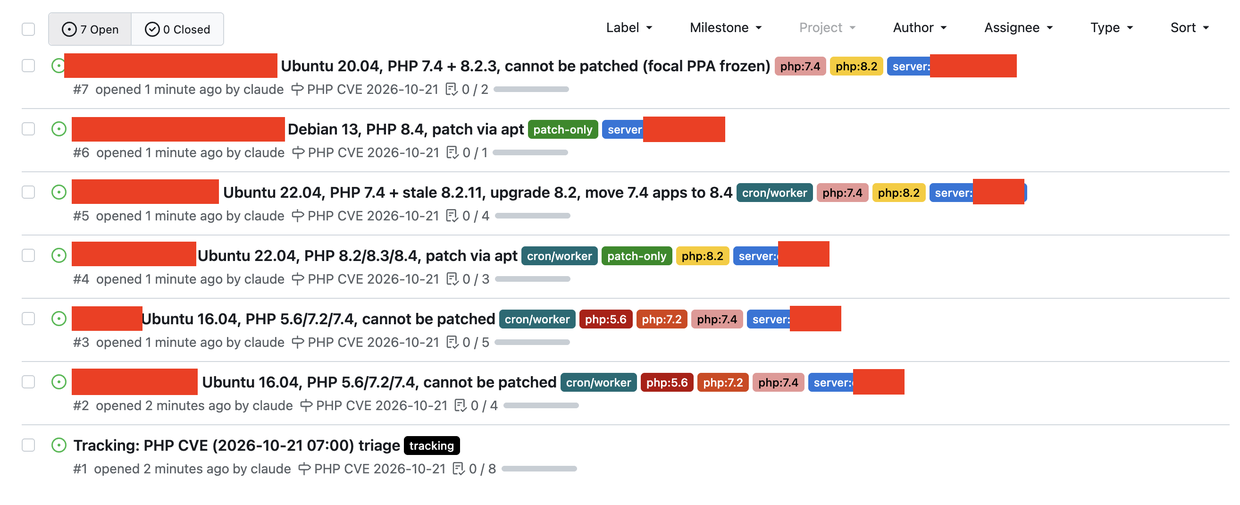
Massive PHP CVE drops tomorrow.
This is what deferred maintenance looks like. This is why I've been working through the backlog of my projects. I've been either using Claude to upgrade them to a modern PHP version, or archiving them as static HTML.
Claude was also able to put this report together for me in about 5 minutes. Now I just have to triage, and yes there will be some hard decisions to make.


WeChat ID
aaronpk_tv
Ok, the quickest way to "fix" this for most of my sites is going to be blocking all POST requests from ever hitting PHP in the first place. Most of my sites are read-only anyway.
The few sites that need to accept POSTs I can allow POST requests only from my home IP address, which is an awkward but feasible workaround for the time being.
nginx, in your
serverblock:if ($request_method = POST) { return 405; }htaccess:
RewriteCond %{REQUEST_METHOD} POSTRewriteRule .* - [F,L]